MSI Is A Global Association Of Over 250 Independent Legal And Accounting Firms In More Than 100 Countries. MSI Has A Successful Track Record Of More Than 25 Years And The Firm Has Recently Been Selected To Represent Mumbai, India.
Please Click Here To See MSI’s Info Graphic Which Highlights Key Facts Of The About. With The Membership At MSI, The Firm Has Now Access To 253 Legal And Accounting Firms Worldwide For Its Clients Who Desire To Do Cross Border Transactions Across The World.
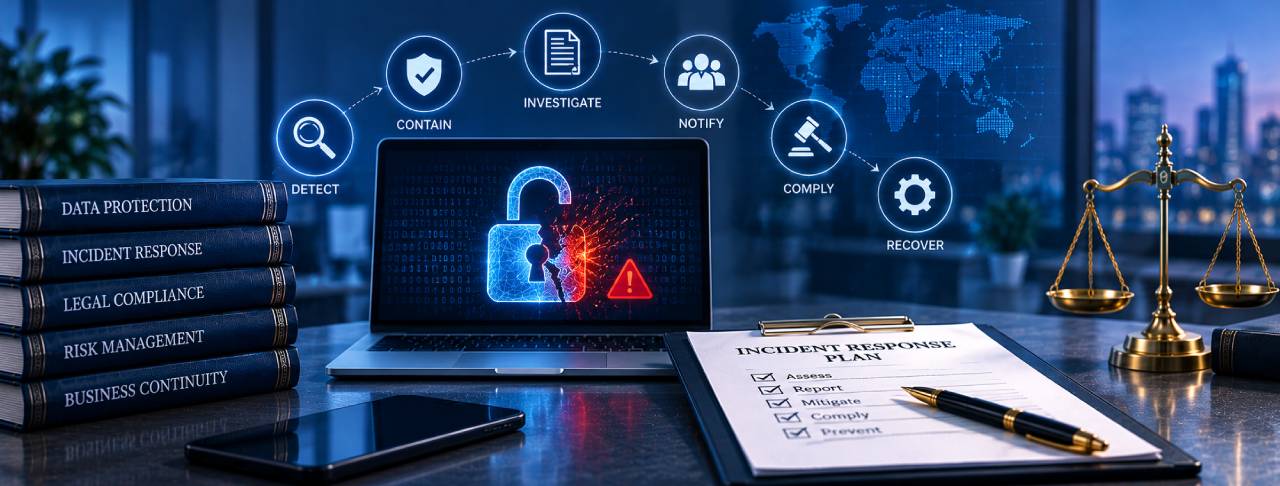
Data Breach Response: Legal Steps Every Business Should Take
A data breach can become a legal, financial and reputational crisis within hours. For Indian businesses, data breach response for businesses now requires more than technical containment. Organisations must assess the incident, preserve evidence, determine applicable reporting duties and coordinate legal, security and business teams. The regulatory landscape is also evolving. India's Digital Personal Data Protection Act, 2023 and the DPDP Rules, 2025 introduce a dedicated framework for personal data breaches, while CERT In continues to impose separate cyber incident reporting obligations.
A strong response therefore starts before an incident occurs. Businesses need a tested response plan, clear responsibilities, reliable logs and a process for making fast legal decisions.
What Is a Data Breach?
A personal data breach generally involves unauthorised processing or accidental disclosure, acquisition, sharing, use, alteration, destruction or loss of access to personal data in a manner which compromises its confidentiality, integrity or availability.
A breach does not always involve a sophisticated cyberattack. A phishing attack, misdirected email, exposed database, stolen laptop, compromised employee account or careless vendor can create a reportable incident.
Businesses should also distinguish between a cybersecurity incident and a personal data breach. A system outage may not involve personal data. A stolen database may involve both a cybersecurity incident and a personal data breach. This distinction matters because different legal and regulatory reporting duties can apply at the same time.
India’s Legal Framework for Data Breach Response
Indian businesses may face several overlapping legal requirements following a security incident.
The Digital Personal Data Protection Act, 2023 creates obligations for Data Fiduciaries concerning reasonable security safeguards and personal data breach notification. Section 8 requires a Data Fiduciary to take reasonable security safeguards to prevent personal data breaches. Section 8(6) also provides for intimation of a personal data breach to the Data Protection Board and affected Data Principals.
The DPDP Rules, 2025 provide operational detail concerning breach notifications. Rule 7 requires a Data Fiduciary, on becoming aware of a personal data breach, to notify affected Data Principals without delay. The Data Protection Board must also be informed without delay, followed by detailed information within 72 hours unless a longer period is permitted.
However, businesses should not assume the DPDP regime has replaced all existing cyber incident requirements. The CERT In Directions issued under Section 70B of the Information Technology Act, 2000 continue to require specified cyber incidents to be reported within six hours of noticing the incident or being informed about it. CERT In expressly identifies data breaches and data leaks among incidents requiring reporting.
The result is a potentially overlapping reporting environment.
The Two Regulatory Clocks Businesses Must Understand
One of the most important practical lessons for businesses is to avoid treating breach reporting as a single deadline.
The CERT In framework operates on a six hour reporting requirement for covered cyber incidents. CERT In's official FAQs clarify that an organisation may initially provide the information available within the reporting period and supplement it later. This means uncertainty about the full scope of an incident should not automatically become a reason for delaying a required report.
The DPDP Rules create a separate process for personal data breaches. Affected Data Principals must be informed without delay. The Data Protection Board must also receive an initial intimation without delay, followed by detailed information within 72 hours, subject to the applicable rules and any extension permitted by the Board.
Businesses should therefore build their incident response process around parallel regulatory assessments, rather than waiting for one investigation to finish before considering another reporting obligation.
Step One: Activate the Incident Response Team
The first legal step after detecting a potential breach is to activate the organisation's incident response structure.
The team should normally include representatives from information security, IT, legal, compliance, senior management and communications. Depending on the incident, HR, finance, insurance, forensic specialists and external counsel may also be required.
One person should have clear authority to coordinate the response. Confusion over responsibility can waste valuable time during the first few hours.
Businesses should maintain an updated contact list for legal counsel, forensic specialists, cybersecurity providers, insurers, CERT In and relevant sector regulators. CERT In itself recommends maintaining current contacts and having response arrangements in place before an incident occurs.
Step Two: Contain the Incident Without Destroying Evidence
Containment is essential, but businesses should avoid making rushed technical changes which destroy useful evidence.
The security team may need to isolate affected systems, disable compromised accounts, revoke credentials, block malicious access and preserve affected infrastructure.
Legal and forensic teams should coordinate evidence preservation. Relevant logs, access records, emails, system images, authentication records and communications should be retained where appropriate.
This is particularly important if litigation, regulatory proceedings, insurance claims or law enforcement investigations may follow.
CERT In has specifically advised organisations to preserve logs when suspicious activity is identified and to report relevant information as required.
Step Three: Establish What Happened
The next stage is incident classification.
The organisation should determine when the incident began, when it was detected, which systems were affected and whether unauthorised access actually occurred.
The investigation should identify the categories of information involved. Customer contact details create different risks from financial information, identity documents, authentication credentials, health information or information relating to children.
The organisation should also establish whether the information was merely exposed, actually accessed, copied, altered, destroyed or transferred.
A preliminary assessment should be documented even when the investigation remains incomplete.
Step Four: Determine Whether Personal Data Is Involved
Not every cyber incident creates a personal data breach.
For example, a denial of service attack may disrupt business operations without exposing personal information. Conversely, a compromised employee account may provide access to customer records even if no evidence of mass extraction has yet been found.
Businesses should therefore map affected systems to the categories of personal data stored within them.
The assessment should also consider whether the organisation is a Data Fiduciary, whether another entity is involved as a Data Processor and whether the affected data belongs to customers, employees, applicants, suppliers or other individuals.
This distinction can affect contractual responsibilities and notification strategy.
Step Five: Assess CERT In Reporting Obligations
Businesses covered by the CERT In Directions should assess whether the incident falls within the specified reporting categories.
The official CERT In Directions require covered entities to report specified cyber incidents within six hours of noticing them or being brought to notice.
The official CERT In FAQs further clarify that data breaches and data leaks fall within the incidents requiring reporting. They also recognise situations where all information may not be available within the initial six hour period. Available information can be provided first, with additional information supplied later.
Businesses should therefore avoid waiting for a perfect forensic report before making a legally required preliminary report.
CERT In Cyber Security Directions and official guidance
Step Six: Assess DPDP Notification Requirements
Where the DPDP Act and Rules are applicable, the organisation must assess its obligations towards affected Data Principals and the Data Protection Board.
Rule 7 requires affected Data Principals to receive information without delay. The notification should explain the nature, extent and timing of the breach, likely consequences, mitigation measures, safety steps the individual can take and relevant contact information.
The Board notification process requires an initial intimation without delay and a detailed report within 72 hours, subject to the possibility of an extension permitted by the Board.
This makes advance preparation extremely valuable. Businesses should maintain draft notification templates and an internal approval process before an incident occurs.
Step Seven: Consider Sector Specific Reporting Duties
A breach may trigger obligations beyond the general cyber and data protection frameworks.
Banks and financial institutions may have reporting requirements under RBI regulations. Listed entities may face SEBI requirements. Insurance businesses may have IRDAI obligations. Other regulated sectors can have their own incident reporting frameworks.
A business should therefore maintain a regulatory matrix covering the sectors and jurisdictions in which it operates.
A single incident can create several reporting obligations with different thresholds, authorities and deadlines.
Step Eight: Manage Third Party and Vendor Breaches
Many businesses assume a vendor breach is solely the vendor's problem.
This approach can create serious legal risk.
Cloud providers, payroll companies, SaaS platforms, payment processors, marketing providers, background verification agencies and outsourced IT providers may process personal data on behalf of a business.
The organisation should therefore know which vendors hold personal data and how quickly they must report incidents to the business.
Vendor contracts should contain appropriate incident notification, cooperation, security, investigation, evidence preservation and remediation provisions.
A business should also maintain an escalation process for vendor incidents so legal and security teams are notified immediately.
Step Nine: Preserve Legal Privilege Where Appropriate
A serious breach can lead to regulatory inquiries, litigation, customer claims and insurance disputes.
Businesses should consider involving legal counsel early. Legal counsel can help structure the investigation, identify reporting obligations, manage communications and assess potential exposure.
The organisation should also distinguish legal advice from ordinary technical or operational communications. Confidentiality and privilege considerations can become complicated if investigation material is widely circulated internally.
A clear legal response structure can help reduce unnecessary disclosure of sensitive investigative information.
Step Ten: Control External Communications
A breach creates pressure to communicate quickly. Speed matters, but accuracy matters too.
Businesses should avoid making speculative statements about the cause, number of affected individuals or identity of attackers before the facts are established.
Customer notifications should be clear, factual and useful. Individuals should understand what happened, what information may be affected, what the business has done and what protective steps they should consider.
Communications should be coordinated between legal, security, management and public relations teams.
Overly technical language can confuse customers. Overly reassuring language can create credibility problems if later facts are different.
Step Eleven: Assess Contracts and Insurance
A breach can trigger contractual obligations even when no regulator becomes involved.
Customers may require immediate notification under commercial agreements. Technology vendors may have contractual incident reporting duties. Insurance policies may contain strict requirements concerning notification, approved forensic providers and cooperation.
Businesses should therefore review relevant contracts and cyber insurance policies as part of the response.
Failing to follow contractual or insurance procedures can create additional financial exposure.
Step Twelve: Document Every Major Decision
Incident response is not only about what the organisation does. It is also about demonstrating why it made particular decisions.
Businesses should maintain an incident chronology recording key events, assessments, notifications, containment measures and remediation steps.
The record should explain important decisions such as why a notification was made, why a particular regulator was contacted, what information was initially available and how the organisation responded as new facts emerged.
Good documentation can become valuable evidence of responsible governance.
Penalties for Data Breach Failures
The financial consequences under the DPDP Act can be substantial once the relevant provisions become operative.
The Schedule to the Act provides for penalties of up to ₹250 crore for failure to take reasonable security safeguards to prevent personal data breaches. Failure to notify the Board or affected Data Principal can attract a penalty of up to ₹200 crore.
These figures represent statutory maximum penalties rather than an automatic fine for every incident.
Businesses should also consider the wider consequences. A breach can cause customer claims, contractual disputes, regulatory scrutiny, operational disruption, investigation costs and reputational damage.
The Importance of a Pre Incident Response Plan
The best time to design a breach response plan is before an incident occurs.
A useful plan should identify the incident response team, escalation procedures, forensic contacts, legal contacts, notification templates, regulatory contacts, communication protocols and evidence preservation requirements.
The plan should also distinguish between cyber incidents and personal data breaches.
CERT In has recommended structured incident response planning, regular cyber drills and post incident reviews.
Tabletop exercises can reveal practical weaknesses. For example, a company may discover during a simulation that nobody knows who can approve a regulatory notification or which vendor holds the affected database.
Post Incident Remediation
Closing the incident is not the same as completing the response.
After containment, the organisation should determine the root cause and identify control failures.
Was the breach caused by a stolen password? Was multi factor authentication missing? Did a vendor have excessive access? Was sensitive data stored without adequate protection? Did employees lack appropriate training?
The organisation should convert these findings into corrective actions with owners and deadlines.
Post incident remediation can include access control changes, security testing, employee training, vendor reassessment, policy updates and system redesign.
The organisation should also consider whether its data breach compliance framework needs to be updated based on lessons from the incident.
How Businesses Can Reduce Future Breach Risk
Effective prevention begins with understanding where personal data exists.
Businesses should maintain data inventories, restrict unnecessary access, establish retention rules and regularly review third party access.
Technical safeguards should be supported by governance. Security controls are less effective when nobody knows who owns the underlying risk.
Regular testing is also important. Businesses should assess their applications, cloud infrastructure, authentication systems and APIs for weaknesses.
Employee awareness remains equally important. Phishing, credential theft and social engineering continue to create significant risks.
Incident response should therefore form part of broader corporate risk management, rather than being treated as an IT only function.
Current Position During DPDP Implementation
Businesses should be careful when describing the DPDP Act as fully operational.
The Government notified the DPDP Rules, 2025 on 13 November 2025 and adopted a phased commencement structure. The core provisions concerning processing obligations, rights and several substantive duties have a later commencement date under the notification.
This does not mean businesses should wait.
CERT In's existing cyber incident reporting framework continues to matter now. Businesses may also have contractual and sector specific obligations independent of the DPDP Act.
The transition period is therefore an opportunity to build a mature incident response system before the full DPDP compliance regime becomes operational.
Conclusion
A data breach should never be treated as only an IT problem. It can quickly become a legal, regulatory, contractual and reputational event.
The most effective data breach response for businesses combines technical containment with legal assessment, evidence preservation, regulatory reporting and controlled communications.
Indian businesses should pay particular attention to the different regulatory timelines. CERT In reporting can require action within six hours for covered cyber incidents, while the DPDP Rules provide separate notification requirements for personal data breaches.
Preparation is therefore critical. A tested incident response plan, clear ownership, reliable logs, vendor controls and prepared notification procedures can significantly improve an organisation's ability to respond when an incident occurs.
Frequently Asked Questions
What should a business do immediately after discovering a data breach?
The business should activate its incident response team, contain the incident, preserve relevant evidence, assess whether personal data is involved and identify applicable regulatory reporting requirements. Legal counsel and forensic specialists should be involved where appropriate.
Does every data breach have to be reported to CERT In?
Not every operational problem is necessarily a reportable cyber incident. Businesses should assess the incident against the categories covered by the CERT In Directions. CERT In's official guidance expressly includes data breaches and data leaks among incidents requiring reporting.
How quickly must a business report a cyber incident to CERT In?
Covered cyber incidents must generally be reported to CERT In within six hours of noticing the incident or being brought to notice.
What is the DPDP breach notification timeline?
Under Rule 7 of the DPDP Rules, 2025, affected Data Principals must be notified without delay. The Data Protection Board must also be informed without delay, followed by detailed information within 72 hours, subject to the applicable rules and any extension permitted by the Board.
Can a company wait until the investigation is complete before reporting?
Not necessarily. Waiting for a complete forensic investigation can create regulatory risk where a reporting deadline has already started. CERT In specifically permits available information to be submitted initially, with additional information provided later.
Who should lead a data breach response?
The response should be coordinated through a designated incident response structure involving security, IT, legal, compliance and senior management. The appropriate participants will depend on the nature and scale of the incident.
What if a third party causes the breach?
The business should immediately assess the vendor's contractual duties, contain the incident, obtain relevant evidence and determine whether the business itself has notification or regulatory obligations. Vendor contracts should include clear incident reporting and cooperation requirements.
Should customers always be notified after a data breach?
Customer notification depends on the applicable legal and regulatory framework and the nature of the incident. Where the DPDP Rules apply, affected Data Principals must be notified without delay in accordance with Rule 7.
What penalties can apply for failing to report a personal data breach under the DPDP Act?
The DPDP Act provides for a penalty of up to ₹200 crore for failure to notify the Board or affected Data Principal of a personal data breach. Failure to take reasonable security safeguards can attract a penalty of up to ₹250 crore.
Is a data breach response plan legally necessary?
A written response plan is an important governance measure even where a particular law does not prescribe a document with that exact title. CERT In guidance encourages structured incident response planning, cyber drills and post incident reviews.
How can businesses prepare for the DPDP breach notification requirements?
Businesses should map personal data, identify responsible teams, establish escalation procedures, prepare notification templates, review vendor contracts, establish evidence preservation procedures and conduct tabletop exercises.
Does the DPDP Act replace CERT In reporting?
No. The two frameworks address different aspects of the regulatory environment. Businesses may have obligations under both, depending on the nature of the incident and their activities. CERT In's six hour reporting requirement can operate alongside DPDP breach notification requirements.
The information contained in this communication is intended solely for the use of the individual or entity to whom it is addressed and others authorized to receive it. This communication may contain confidential or legally privileged information. If you are not the intended recipient, any disclosure, copying, distribution or action taken relying on the contents is prohibited and may be unlawful. If you have received this communication in error, or if you or your employer does not consent to email messages of this kind, please notify the sender immediately by responding to this email and then delete it from your system. No liability is accepted for any harm that may be caused to your systems or data by this message.
OUR CLIENTS
MEDIA COVERAGES
AWARDS & RECOGNITION


AFFILIATIONS & ASSOCIATIONS
MEMBERS OF MSI GLOBAL ALLIANCE
MEMBERS OF ILF
International Law Firms (ILF) Is An International Association Of Independent Smaller And Mid-Sized Law Firms Serving Their Clients’ Needs In Cross Border Business Legal Issues. Our Association With ILF Enables Us To Effectively Assist Clients With Trans-National Legal Issues At Effective Prices.
LIFE AT MHCO


PRACTICE AREA
Private Limited Company Registration in India
Setting up a Company in India
Foreign Direct Investment (FDI) in India
Foreign Business Registration in India
Small Business Registration in India
GET IN TOUCH
Mumbai: Surya Mahal, 2nd Floor 5, Burjorji Bharcha Marg Fort, Mumbai-400 023 India
Contact No.: T: +91-22-40565252
E: contact@mhcolaw.com
Delhi: C-9, Lower Ground Floor Jangpura Extension, New Delhi-110 0014 India
Contact No.: T: +91-11-40196496
E: contact@mhcolaw.com
Contact No.: T: +91-22-40565252
E: contact@mhcolaw.com
Delhi: C-9, Lower Ground Floor Jangpura Extension, New Delhi-110 0014 India
Contact No.: T: +91-11-40196496
E: contact@mhcolaw.com
2025 - MANSUKHLAL HIRALAL & CO.
Need Help? Chat with us